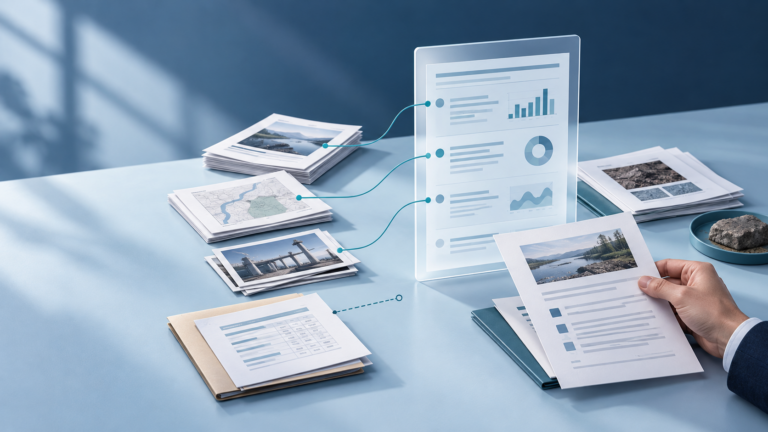
At a glance
- The risk: A polished AI-assisted assessment can make incomplete evidence look complete.
- The governance implication: Reviewers need traceability to sources, assumptions and gaps—not only plausible prose.
- The leadership takeaway: Name who owns evidence sufficiency before the output becomes an official decision record.
When AI helps produce a cybersecurity profile or governance assessment, the consequential decision is not whether the tool saves time. It is whether leaders should rely on the resulting picture of risk.
A clear, executive-ready output does not make the evidence complete. If the organization cannot show which facts support each conclusion, which gaps became assumptions and who approved those judgments, a faster assessment may produce a weaker decision.
A Faster Assessment Can Still Create a Weaker Decision
Assessment work compresses policies, tickets, interviews and technical records into findings and priorities. AI can accelerate that synthesis, but it also increases the distance between source material and final judgment.
A model may organize partial evidence into a persuasive narrative. Reviewers can then mistake coherence for substantiation, especially when the output resembles familiar audit language. A check that asks whether the report sounds reasonable may not test whether each material claim is traceable to adequate evidence.
What NIST’s Draft Actually Proposes
Verified source facts: On 19 August 2026, the U.S. National Institute of Standards and Technology released an initial public draft of SP 1353, a guide for using AI in Cybersecurity Framework analysis and reporting. Comments are due 15 October 2026.
The draft describes three notional uses: governance review, a current-state profile, and a target-state profile. It tells users to validate scope, inputs, assumptions and outputs; preserve traceability; distinguish documented process from observed practice; and have qualified personnel review AI-generated content. These are possible approaches, not prescriptive assurance methods. The draft is neither a new binding requirement nor approval of a particular tool.
The Risk Is Not Only Hallucination
Hallucination matters, but the harder problem is unsupported completeness. The system may accurately summarize what it received while the evidence set is incomplete, stale or biased toward documented controls.
Fact-checking prose will not reveal an interview that never happened, a control that was documented but not observed, or a business unit missing from scope. Editorial interpretation for review: an AI-assisted assessment should carry an evidence ledger. Each material conclusion should identify its source, uncertainty and whether it reflects documentation, observation or inference.
An Illustrative Financial-Services Scenario
Illustrative scenario—not a client case: A financial-services firm asks an approved AI tool to assemble a current-state cybersecurity profile from policies, selected control records and staff interviews. The polished draft informs next year’s investment priorities.
Later, the risk team finds operational exceptions stored outside the approved evidence set. The AI did not invent a fact; it synthesized an incomplete boundary. The decision failed because nobody owned the question, “Is this evidence sufficient for the investment decision?” That ownership belongs with the leader authorized to accept the scope and consequences. Risk and assurance functions need authority to pause approval when provenance or material gaps cannot be resolved.
Keep Evidence Separate From Interpretation
Before AI drafts the report, leaders should define the evidence standard. Require source-level traceability, a visible “not evidenced” state, and separate fields for facts, assumptions and proposed mappings. Preserve the prompt, source list, tool version, review comments and approvals as part of the decision record.
Oversight should occur before the output becomes the official baseline or target state. Reviewers should test high-impact conclusions back to source material and ask what was excluded. This is more demanding than a final copy edit, but it is where oversight can still change the decision.
Questions for the Leadership Team
- Who decides that the evidence set is sufficient for the business decision this assessment will support?
- Can a reviewer trace each material conclusion to a source, and see where documentation, observation and inference differ?
- Who can pause approval when evidence gaps are material, even if the report appears complete?
Closing Thought
AI can make risk analysis faster without making the evidence stronger. Governance must preserve the boundary between what is known, inferred and untested. Leaders should decide who owns that boundary before a polished draft shapes budgets, priorities or risk acceptance.
Sources and Further Reading
- NIST SP 1353 (Initial Public Draft) — published 19 August 2026; comments due 15 October 2026.
- Official NIST draft PDF and DOI record.
- NIST AI Risk Management Framework — voluntary framework and revision information.
- Beyond1n0: AI Assurance.
- Beyond1n0: Your AI Vendor Has Documentation. Do You Have a Defensible Decision?.
About Gary
Gary Cheung writes about decision accountability, design-phase governance and executive judgment in AI and information risk. Contact Gary.